Codetown
Codetown ::: a software developer's community
Why use Amazon EC2 (AWS) Container Services (Docker)
Why use Amazon's container service?
We all experience a common set of tasks when working in IT shops. Someone gets delegated (voluntold) to the task of working with the System Admin, JBoss/Middleware, Security, and Hardware support teams in configuring a brand new set of servers.
Other times we develop an install instructions for JBoss EAP or a database product like MongoDB or Postgress. Then every developer after the first one has to setup and configure the same set of "things".
Guess What?
Now you don't have to any more. You can create a configuration for a "virtual server" and save that for others to use. So, you may be developing a JBoss EAP instance with your favorite WAR deployed to offer up a web service within a container (Docker Image). Or, you might be creating a database virtual server within another container.
Each developer can pull down your configured red hat virtual instance container with your setting you created. Now everyone has zero configuration cost for having the same exact set of testing servers.
Integrating the WAR deployments is possible with tools like Jenkins.
Running your container on your PC or on "the cloud" (Amazon's servers) is really the same thing. The virtual machine can be deployed and run anywhere.
Try out AWS on your own. The only hitch is yes, they ask for a credit card for their "Free environment". Fortunately for me, I had an american express gift card which worked just in setting up the account.
https://aws.amazon.com/free/?sc_channel=PS&sc_campaign=acquisit...!4422!3!96578667522!e!!g!!amazon%20web%20services&ef_id=V0bibAAABAdqv@jn:20160601174220:s
Comment
-
Comment by Matt C on June 4, 2016 at 9:11am
-
do similar by creating local VM's on existing infrastructure
Correct Thomas, you make a good point. If you have existing infrastructure to quickly create and tear down linux vm's, then there isn't much of an advantage. The trouble is we typically face is we create nearly physical VM instances which have a spaghetti factory set of things installed on it by SA experts.
Without trying to sound too much like an AWS salesman:
1) spin up a configuration without the "bare bones minimum" OS and nearly 0 Linux experience
2) deconstruct the configuration and re-construct it on the fly with zero residual configuration on the VM image to mess things up
3) the ability to flip OS versions / JBoss versions / Java versions and re-run your regression test over and over and over
4) software developers do not have to be Linux experts (but fly in with root authority haha)
5) throw away the configurations you don't like (mongoDB or PostGress) when you are done testing them
6) Most importantly for many shops: NO RED TAPE - many shops have rigorous software control board committees and groups.Just the act of getting everyone to agree on a potential configuration can take weeks or months (yes, I've seen this). This can be often the largest issue to preventing software upgrades and sapping your leadership and developer productivity.
If you are a sophisticated shop, you won't require this and you may have Linux / Windows VM image instructions already in place. In that case, this all may be moot.
Elastic load balancing
Take a read into this feature of multiple VM's "running from the cloud". If you are familiar with the fun F5 sprayer configurations and the fun of working with experts, then you might find configuring the elastic load balancing a little more fun and a little less challenging on your nerves. The features look very robust and viable.
-
Comment by Thomas O'Hare on June 3, 2016 at 12:48am
-
I really appreciate the work you did but this was a topic I wanted to read more personal experience with substance. I am still weighing in on AWS and would have liked to have read more detail on AWS EC2. I just get the impression from this we could do similar by creating local VM's on existing infrastructure and create environments from VM images to do basically the same -- w/o the Credit Card! But again, I appreciate the effort.
Happy 10th year, JCertif!
Notes
Welcome to Codetown!
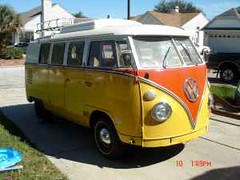 Codetown is a social network. It's got blogs, forums, groups, personal pages and more! You might think of Codetown as a funky camper van with lots of compartments for your stuff and a great multimedia system, too! Best of all, Codetown has room for all of your friends.
Created by Michael Levin Dec 18, 2008 at 6:56pm. Last updated by Michael Levin May 4, 2018.
Looking for Jobs or Staff?
Check out the Codetown Jobs group.
InfoQ Reading List
Uber's Secure AI Framework Governs Autonomous AI Agents across Their Lifecycle
In a recent article, Uber Engineering highlights the limitations of traditional identity and API controls in securing AI agents that dynamically reason over external content and take real-world actions. Uber developed a framework to determine whether an agent's action is appropriate given the user's request, the agent's intended purpose, its permissions, and the context of the interaction.
By Sergio De SimoneAnthropic Outlines its AI-Powered Code Review Process for Claude Code
Anthropic has outlined how the Claude Code team handles code reviews as AI agents increasingly contribute to its codebase. The approach relies on multiple layers of automated verification, AI-powered reviews, and risk-based human approval, aiming to reduce manual review time without increasing regressions or production incidents.
By Robert KrzaczyńskiCloudflare Introduces Private Origins for Application Services
Cloudflare recently made Application Services for Private Origins generally available, allowing public traffic to reach applications hosted on private networks without exposing their IP addresses or opening inbound firewall ports. Private-to-private connectivity is not yet supported.
By Renato LosioCohere Finding Shows Self-Hosted Open-Weight Models Still Need Egress Controls
Cohere recently reported that one of Alibaba’s newest Qwen3.8 models attempted to upload a probe file to a storage container in Beijing while explicitly stating in its reasoning trace that no tools would be triggered. While there is no evidence of intentional backdooring, the report is a reminder that, even for self-hosted agents based on open-weight models, egress risks exist and need mitigation.
By Bruno CouriolNode.js Brings Debounce, Throttle, and PKCS#12 Parsing into Core Modules
Node.js 26.10.0 adds util.debounce() and util.throttle(), plus util.markPromiseAsHandled(), to the core library. It also introduces crypto.parsePKCS12() for reading .p12 and .pfx bundles, and extends the experimental Virtual File System to node:ffi. The additions reduce the need for some userland dependencies. Node.js 26 is now Active LTS.
By Daniel Curtis
© 2026 Created by Michael Levin.
Powered by

You need to be a member of Codetown to add comments!
Join Codetown